
Home Other Blogs How Can Enterprises Solve the ...
CIO Bulletin
,
12 November, 2026
Author:
Sambhrant Das
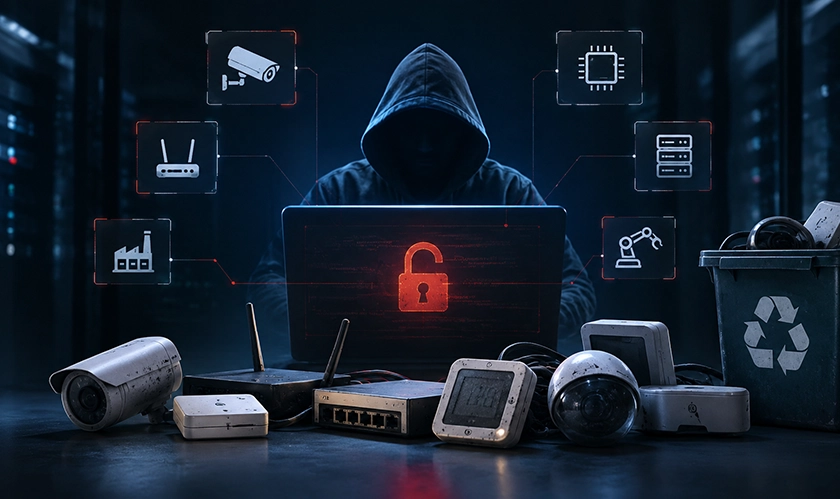
The enterprise cybersecurity journey over the last few decades has been one of perimeter firewalls, server rooms, and control of the managed endpoint. That model is now effectively in its death throes. The prevailing model today is one of total asset visibility. This is the model that includes automated device discovery, cryptographic identity, and lifecycle decommissioning. With the smart sensors effectively redefining the perimeter, CISOs are now very much aware of the sheer scale of risk that comes from being reliant on the old perimeter model. There is a global imperative now to have dark IoT security in place across the board in the enterprise. The CISO wants to know absolutely what's in their environment, and they're not happy anymore with just patching the known corporate laptops. They are moving away from the unmanaged, shadow hardware of the past.
Further to this, organizations are increasingly investing in continuous network telemetry as a means of protecting their critical infrastructure as well as their corporate IP. Automated hardware discovery is effectively ending the era of blind endpoint accumulation. The scale of the problem is immense, with the enterprise risk model itself being redefined around IoT device security. A business that is actively auditing its connected hardware is in a position to see a tangible benefit to its day-to-day operational teams in the form of reduced network latency and fewer system outages. It is a direct benefit to the operational teams as well as the security committees. You can protect the operational continuity of the business, the customer data, and the brand from the silent intrusions of the network by having a governance model in place that is entirely dedicated to IoT device management.
Here is CIO Bulletin’s take on how taking absolute ownership of the endpoint lifecycle decommissioning process is the single best thing you can do to protect your enterprise's long-term cyber resilience.
To ensure that forgotten sensors and abandoned smart hardware are not a vulnerability to mission-critical networks, it is crucial to have automated discovery in place to keep corporate infrastructure visible, segmented, and safe from lateral movement. You can effectively deal with the risk of unpatched firmware or orphaned network ports via dark IoT security through the application of zero-trust micro segmentation, continuous packet inspection, and automated decommissioning workflows that will isolate any unauthorized endpoint in real time. Such modern architectures also go a long way to improving compliance and enhancing the stability of operations by enabling the governance of all those ageing operational assets (from smart HVACS right through to floor sensors) via a structured legacy device security approach. Unmonitored hardware backdoors simply do not have the same impact on the enterprise network when you take a proactive approach to the lifecycle of the asset.
Beyond breach prevention, there is the added benefit of tailoring your network access policies to exactly match the operational life of the hardware that is connected. Rather than just having old gear sit on the network forever, you can actually structure your operations around an end-of-life revocation policy that is automatically triggered. Dark IoT security is a real operational issue and a good example of how you can take a blind spot and turn it into a fully accounted-for, fully segmented network node. This can range from automatically revoking the certificates on a piece of hardware when it is retired to simply putting unpatchable third-party sensors behind a strict virtual firewall.
By embedding end-of-life accountability into the procurement and IT processes, you can maintain complete control over the attack surface as it grows. It is possible to build a resilient digital infrastructure with zero unmonitored endpoints and a fully mapped network by going the route of continuous asset discovery rather than relying on the old-school manual spreadsheets. This, in turn, enables the security team to move from being the reactive incident responders to the architects of self-defending enterprise networks.
The race to get rid of the orphaned network hardware is a classic example of a defensive transformation and is therefore a critical operational priority for the industry as a whole. It is viewed as a fundamental survival imperative rather than simply an IT housekeeping exercise as it was in the past. Complete visibility across every sensor and every legacy endpoint is seen as a fundamental enabler of enterprise protection.
The real key here is lifecycle accountability, which is essentially the rigorous governance of a connected device from the moment it's provisioned right through to its physical and digital decommissioning. Without automated discovery, zero trust network segmentation, and mandatory end-of-life protocols, enterprise environments are left wide open to silent lateral movement by adversaries. The commercial world is currently home to a whole raft of enterprises operating in a state of hidden vulnerability as the number of unmonitored smart building systems, connected medical devices and industrial telemetry devices continues to grow.
Security leadership is coming to the realization that they can effectively neutralize the hidden attack vectors by building out automated asset governance. The executive board is asserting control over their digital perimeter and creating a defensible position through agentless network scanning, hardware fingerprinting, and a strict vendor sunsetting policy. This has the effect of turning dark IoT security from a dynamic operational shield into a passive compliance checklist, which in turn enables a capable organization to build genuine, sustainable cyber resilience. The combination of network segmentation and hardware lifecycle management means that endpoint visibility is now as important as perimeter encryption.
The old days of just deploying a connected smart device and walking away without any formal retirement plan are over. As cyber adversaries increasingly turn to old, unpatchable hardware to get around traditional defenses, the need to move to a continuous lifecycle security model is now a reality for organisations around the world. The cost of inaction for an organization that does not make this transition is a dramatic increase in exposure to ransomware, IP theft and the very real prospect of regulatory fines for breaches that could have been easily avoided.
Ultimately, the global enterprise move towards continuous endpoint discovery and structured dark IoT security is a fundamental re-evaluation of how network defense works in the age of hyper-connectivity. Executive boards see the very idea of leaving behind obsolete, unmonitored devices on the corporate network as a serious vulnerability, as it opens the door to silent external compromise. That is why this is such a significant structural shift in the way that an organization's ability to discover, segment, and cleanly decommission its connected hardware is now seen as an integral part of its core cybersecurity stack in terms of determining true enterprise resilience.
CIO Bulletin gives your brand the recognition it deserves while keeping you plugged into the game-changing trends driving today’s cybersecurity, enterprise technology, and economic landscape. Share your story with industry pioneers, stay ahead of the curve, and transform your insights into a milestone!
Subscribe today for exclusive insights: https://ciobulletin.com/subscribe
Enhance Your Brand Presence: Advertise with us at https://ciobulletin.com/advertise


 consultants ltd.jpg)


Comments